Comment Section Issues on ArcBlock Marketplace Discussion Page

Summary: On the ArcBlock Marketplace discussion page, the comment system has multiple issues:
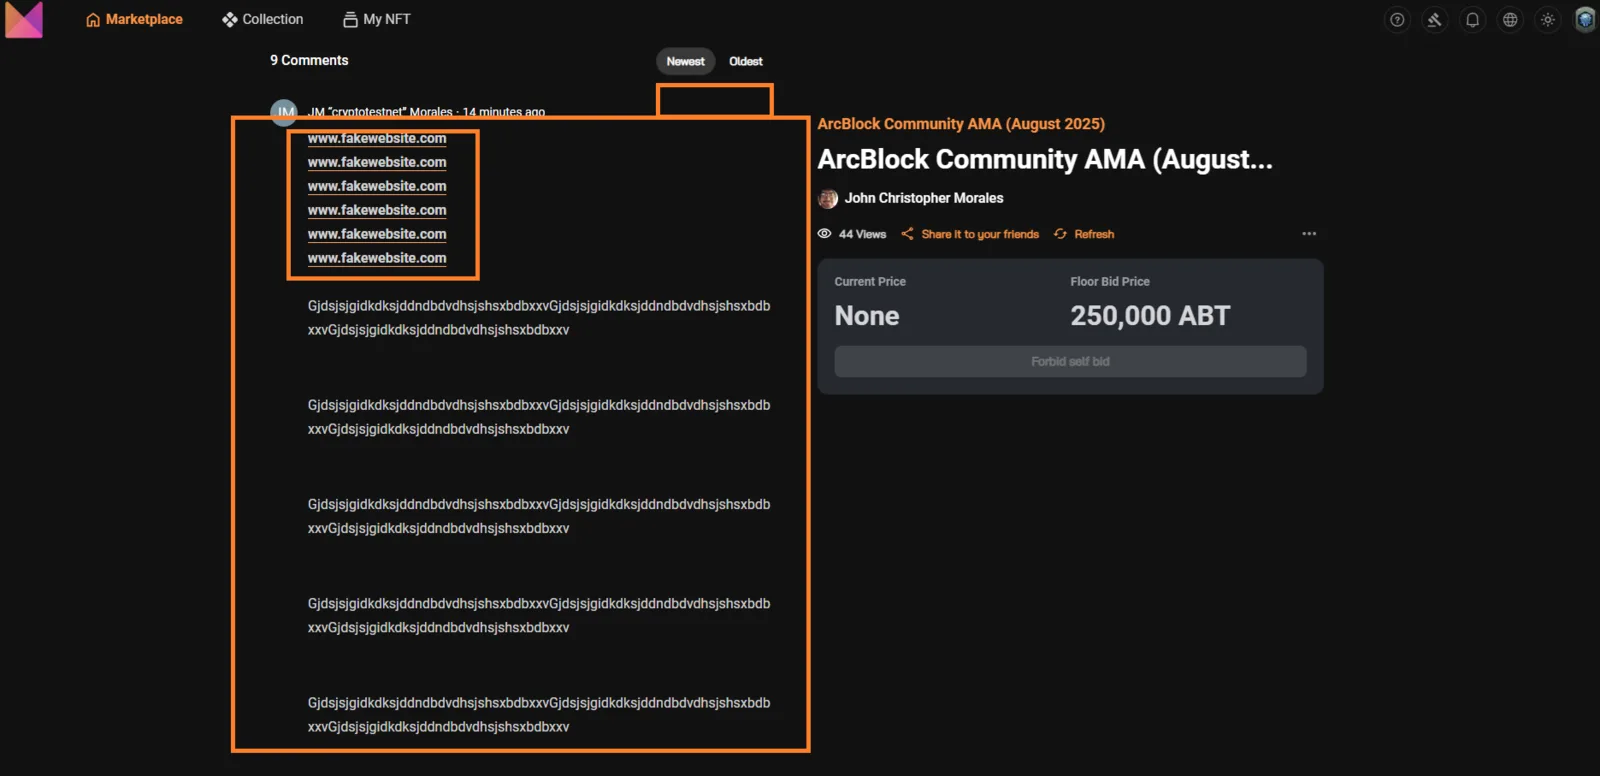
- It allows extremely long comments (up to or beyond 10,000 characters).
- Users can post links to fake or malicious websites without validation or moderation.
- There is no option to block or report users who spam the comments section.
These combined issues can lead to spam, phishing, and community abuse.
Environment:
- Website: ArcBlock Marketplace Discussion
- Browser: Google Chrome (latest)
- OS: Windows 10 / Android
- Account Type: Logged-in DID user
- Network: Stable
Steps to Reproduce:
- Go to: https://marketplace.arcblock.io/did-comments/discussions/zjdwAMpweCnPpcoTkG6SJ5A7u5dtPd8tYFPd#4afec624-4a2a-416f-b33c-106822bea511
- Scroll to the comment section.
- Enter a long text (>1000 characters) and post — it is accepted without restriction.
- Post a comment containing an external link (e.g., fake or phishing website).
- Observe that the link is accepted and clickable.
- Try to find a “Block” or “Report User” option for spam or abuse — none available.
Expected Result:
- Comment character count should be limited (e.g., 500–1000 chars).
- Comments should auto-filter or warn users when posting external or suspicious links.
- A “Block” or “Report” feature should be available for community moderation.
Actual Result:
- Users can post 10,000-length comments.
- Fake or unsafe URLs are not validated or blocked.
- No user control or moderation tools exist for spam prevention.
Impact:
- Enables spam, phishing, and fake site promotion.
- Reduces content quality and credibility of discussions.
- Creates potential security and privacy risks for community members.
Weakness Mapping (CWE):
- CWE-20: Improper Input Validation
- CWE-79: Cross-Site Scripting (XSS) via unsanitized comment input)
- CWE-284: Improper Access Control (no spam moderation features)
- CWE-400: Uncontrolled Resource Consumption (unlimited text input)
Severity Classification:
- 🔴 High Severity
- Security and moderation vulnerabilities — can lead to spam abuse or phishing exposure.
Suggested Fixes:
- Set a character limit for comments (recommended: max 1,000).
- Implement URL validation and filtering — disallow suspicious or non-https links.
- Add a “Block”, “Report”, or “Flag” button for users to report spam accounts.
- Sanitize and escape all user input to prevent XSS injection.
- Log and auto-hide comments containing blacklisted domains or flagged words.
Proof of Concept (POC):
- Test Input 1: Paste a 10,000-character comment — accepted ✅
- Test Input 2: Comment with fake URL
http://malicious-site.xyz— accepted ✅ - Test Input 3: Attempt to block or report spam user — ❌ No option available
⚡ Priority: High (Impacts user trust, security, and community moderation).